Title here
Summary here
Offensive Security Analyst · Aspiring Exploit Developer
July 15, 20253 minutes
Last weekend, at a CTF (l3ack ctf 2025), I came across a simple ret2win, or so it seemed. The code had a gets that stored the input in a 272-character buffer, and there was also a win function that ran /bin/sh, but there was a problem… On the server, the binary wasn’t run directly: the input first went through a Python script that contained the following:
February 24, 20252 minutes
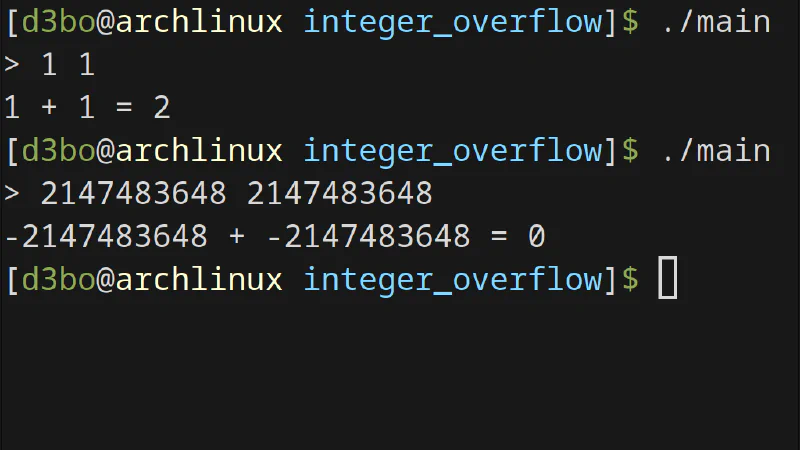
Why is 4294967295 + 1 equal to 0? You will find out in this post...
June 24, 2024 8 minutes | TryHackMe
Throughout this machine, we analyze a binary and exploit a buffer overflow vulnerability that gives us access to the server. For privilege escalation, we extract the credentials stored in Firefox using the Firepwd tool.
June 23, 2024 6 minutes | TryHackMe
In this machine, we exploit a CVE in Tika 1.17 that lets us inject commands on the target machine. For privilege escalation, we abuse the AlwaysInstallElevated setting to get a shell as NT AUTHORITY/SYSTEM.